How to prepare for SOC 2 without an internal compliance team
In about two months, Talsoft helped a U.S. SaaS company assess controls, identify gaps and build a roadmap toward SOC 2 Type I readiness.
Talsoft Blog
Analysis, guides and practical criteria for leaders who need to turn technical risks into business priorities.

In about two months, Talsoft helped a U.S. SaaS company assess controls, identify gaps and build a roadmap toward SOC 2 Type I readiness.

Preparing for ISO 27001 means identifying risks, selecting controls, assigning owners and gathering evidence that your ISMS works.

When an audit is close, distinguish missing proof from partial controls and real gaps so your team can focus on what matters most.

Over approximately six months, Talsoft supported an Australian financial company from assessment to a more operational ISMS with prioritized controls, owners and evidence.

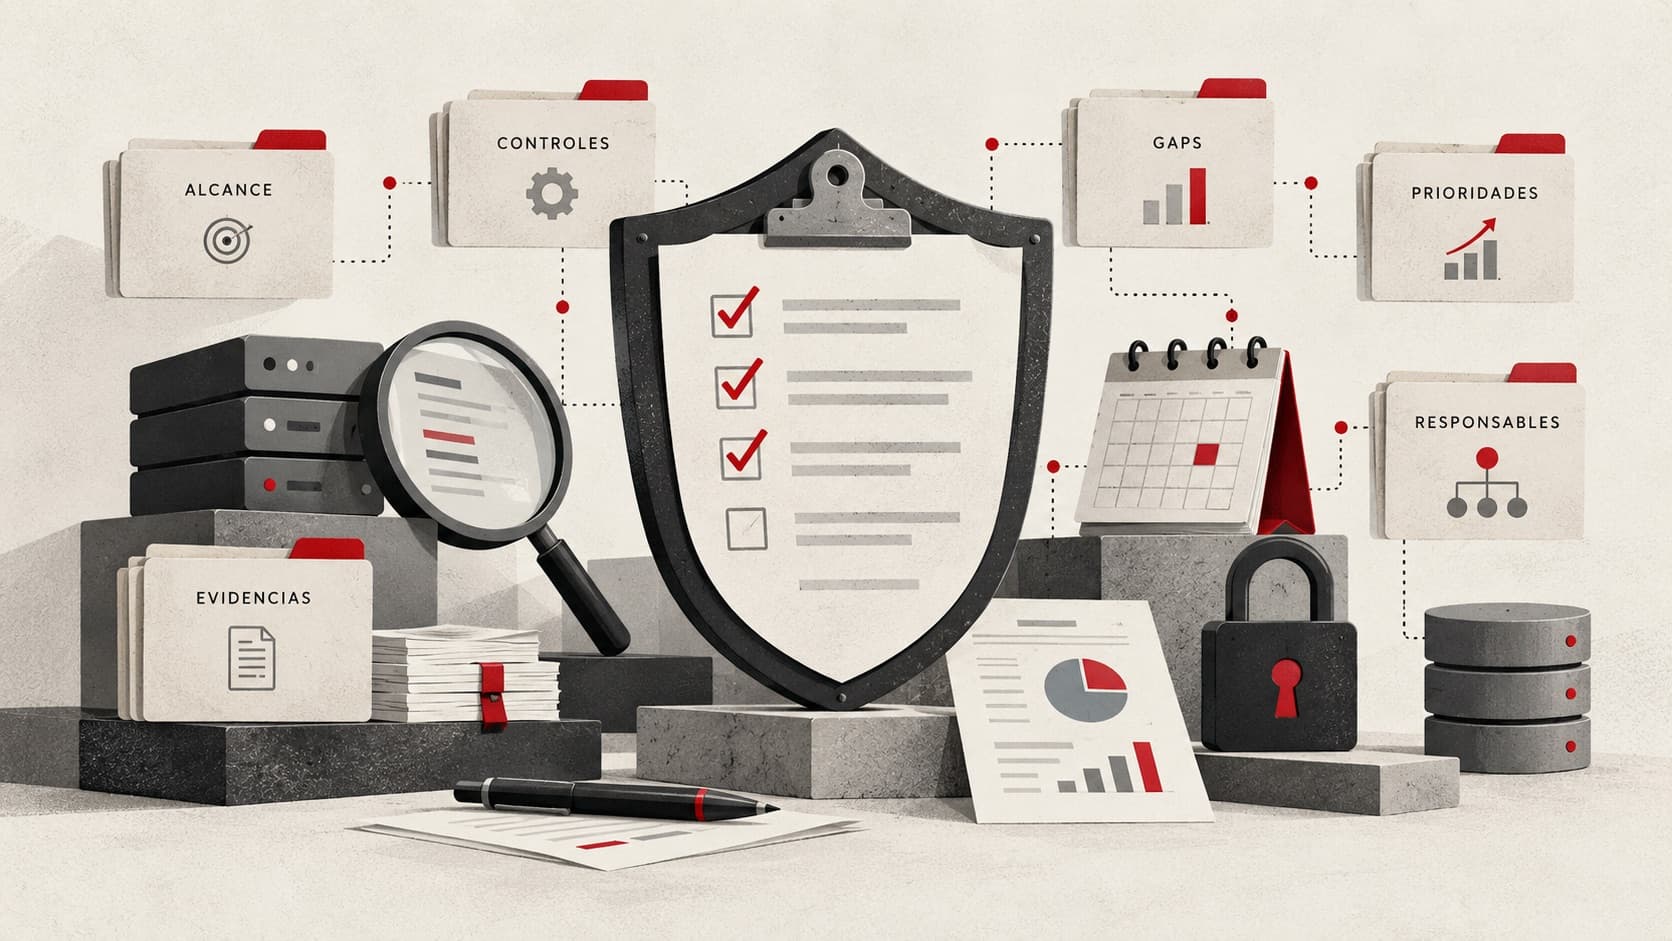
Define the scope, review controls and gather evidence early so your security audit starts with clear priorities and owners.

How to organize owners, controls and evidence to answer a security questionnaire consistently.

Cybersecurity evidence demonstrates that a company’s controls exist, are implemented and work in practice.

How to identify gaps, prioritize risks and turn a cybersecurity assessment into implementation, evidence and continuous improvement.

The controls and evidence companies should prepare to demonstrate how their security operates when working with insurers and brokers.

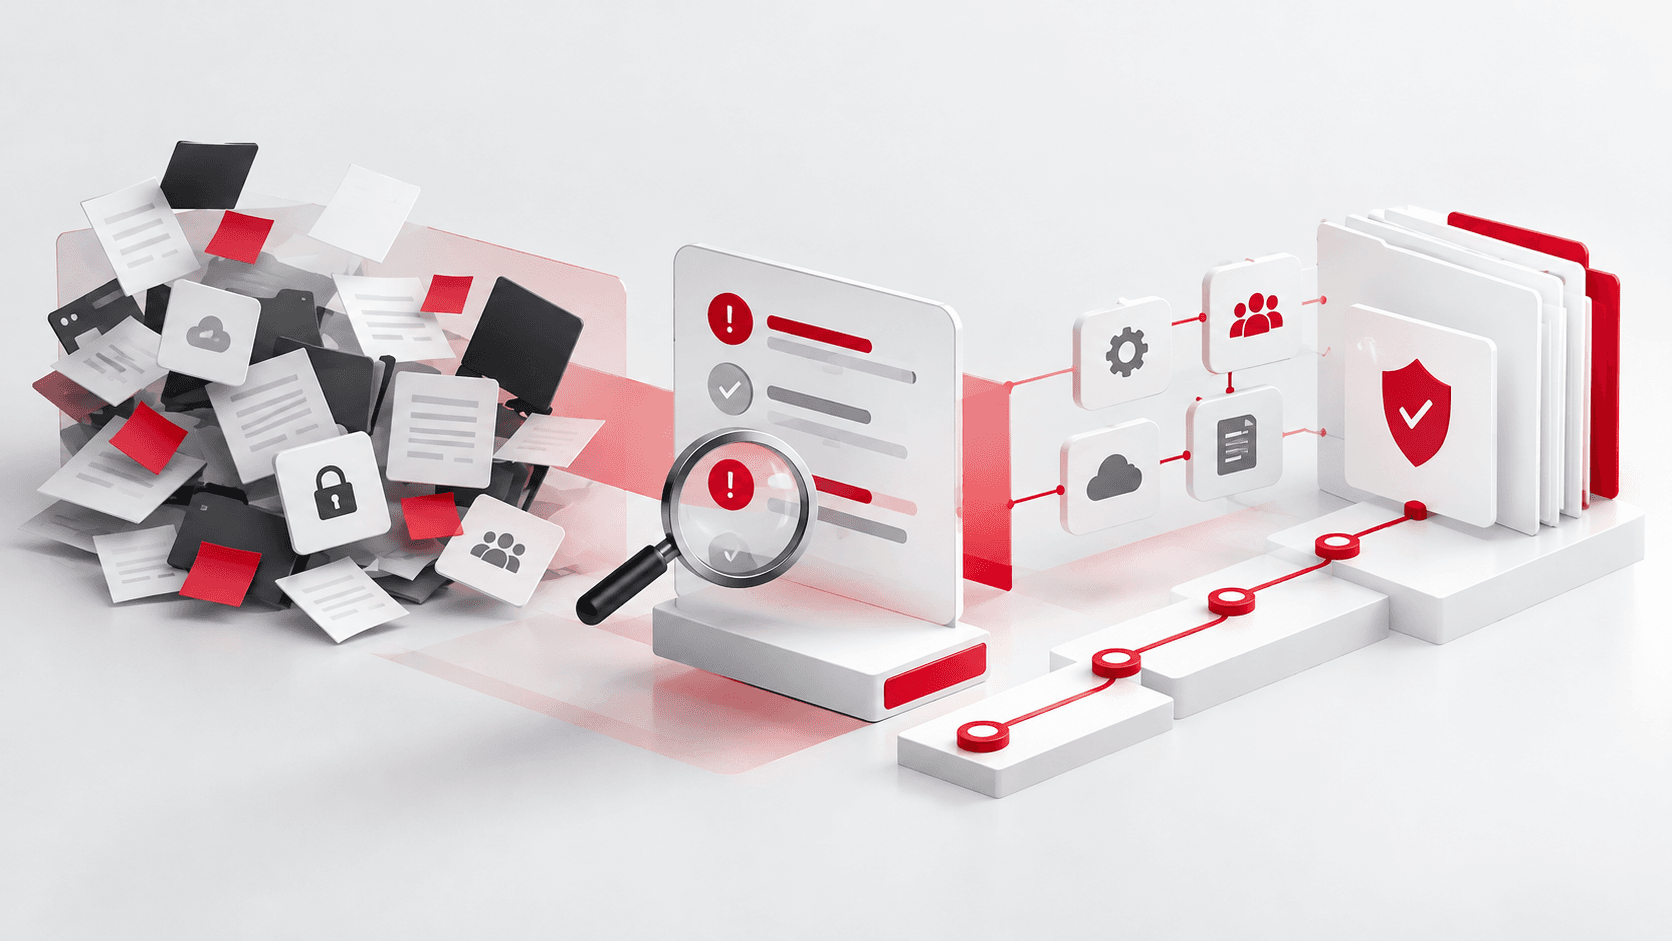
How a maturity partner organizes risks, controls, owners and evidence to turn scattered security initiatives into a sustainable roadmap.

A practical method to turn technical findings into decisions, owners and next steps that leadership can sustain.